Clarity & Control
One framework. Clear responsibilities.
A group-wide approach connects standards, risk assessment, incident handling, controls and management reporting.
ClientGerman organization · more than 500 IT employees
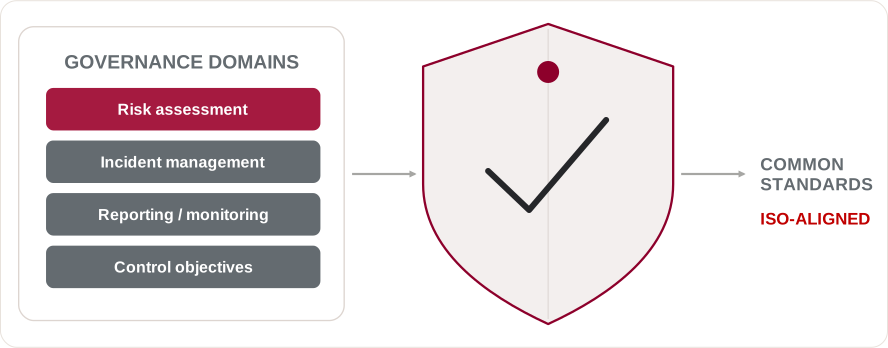 VISUAL MODEL / SCHEMATIC
Understand the situation.
Different business models across several units had produced inconsistent IT security standards and processes.
Design a response.
Specify a common information security governance framework and responsibilities.
Build a basis for action.
A common language for information security.
Connect standards, ownership and oversight.
Different business models across several units had produced inconsistent IT security standards and processes. A coordinated framework and compliance orientation were needed.
The steps summarize the engagement described in SOICON's existing Results materials. They are not performance measurements.
01
Define governance
Specify a common information security governance framework and responsibilities.
02
Establish control areas
Connect risk assessment, incident management and control objectives.
03
Create transparency
Introduce consistent reporting and monitoring of information security activities.
04
Align practices
Coordinate with CIOs and orient standards and routines toward relevant ISO requirements.
A common language for information security.
A defined security governance model with harmonized control areas, reporting principles and orientation toward common information security standards.